Information Risk Management Training
Build understanding of how information risk is identified, assessed and managed, for people who own or contribute to those decisions.
Capability
Strong security capability depends upon people as well as technology.
Talk to us about Training and Development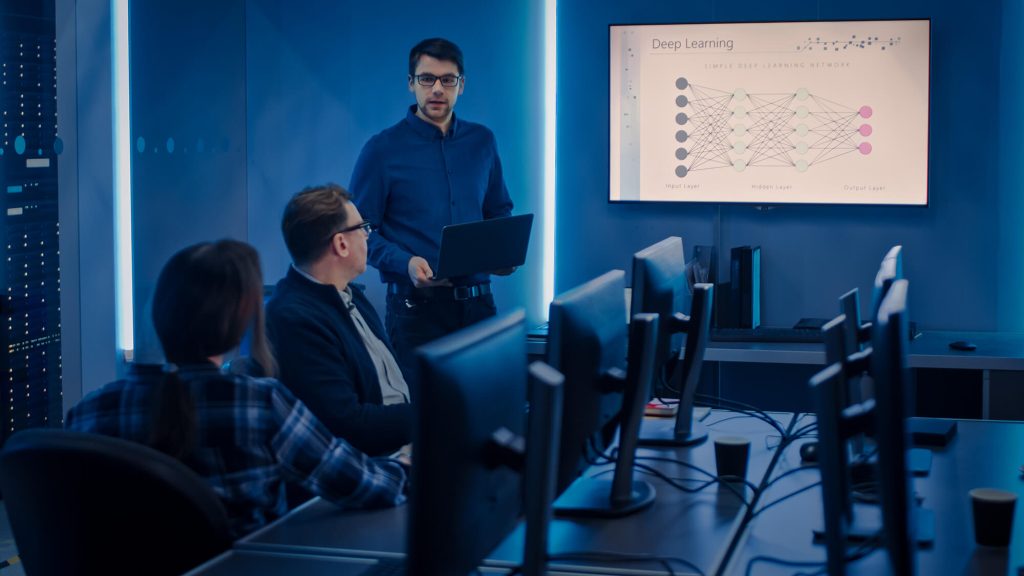
Stanway Hope provides security training and development designed to help individuals and teams improve their understanding of cyber and information security and apply that knowledge within their roles. Training can be aligned to the needs of an organisation, team or audience, helping participants develop knowledge that supports professional development and organisational security objectives.
We offer training and development programmes to meet individual client needs. Content can be shaped around the customer's objectives, audience and existing level of knowledge, so learning focuses on the security challenges most relevant to the people undertaking it, rather than a single off-the-shelf course.
These four programme types are the concrete offering. Each is tailored to the audience rather than copied from a public catalogue.
Build understanding of how information risk is identified, assessed and managed, for people who own or contribute to those decisions.
Development programmes for security specialists who need to deepen or broaden the skills they use in role.
Briefing programmes that raise awareness of security responsibilities across a wider audience, not only the security team.
Briefings focused on how security is carried out in operation, so practice on the ground matches the intent of policy and design.
Shape the learning around the audience, the role and the security work people are expected to support.
Help audiences understand security responsibilities, common risks and the role individuals play in protecting information and services.
Support learning that reflects the security knowledge required for particular responsibilities or areas of work.
Develop understanding of relevant technical security concepts and their application within systems and services.
Develop understanding of security risk management, assurance and associated activities.
Adapt training to the audience, organisational context and required learning objectives.
Help teams develop internal understanding through structured learning and engagement with security practitioners.
Training is useful when people can apply it in the work they already do.
Improved understanding of cyber and information security, matched to the audience rather than a generic syllabus.
Greater confidence in applying relevant security knowledge within the responsibilities people already hold.
Better understanding of individual security responsibilities, including beyond the security team.
Development of security capability within teams and organisations, supporting the security work people are asked to contribute to.
How an engagement may typically progress, shaped around the people taking part.
Identify the audience, existing knowledge and learning objectives.
Develop or select appropriate learning content.
Provide training appropriate to the audience and subject.
Consider learning outcomes and opportunities for further development.
Training can support capability across risk, architecture and assurance work. Services can be taken individually or combined.
Identify and understand security risk, including where teams need stronger risk-management knowledge.
Explore service
Help teams understand how security is designed into the systems and services they work with.
Explore service
Plan and present assurance evidence, supported by people who understand the security decisions they are making.
Explore serviceTell us who the audience is and what they need to be able to do. We can discuss a programme that fits, rather than a generic course.